Three services

Pick the question you need answered.

Compromise assessment

Has someone already been in?

  • Persistence mechanisms
  • Malicious indicators
  • Signs of previous compromise
  • Dormant access and tooling
Threat hunt

Are we exposed to what is active right now?

  • Hunts built from your sector, suppliers and stack
  • Current trending IOCs
  • Current TTPs, mapped to MITRE ATT&CK
  • Specific threat actors on request
Hygiene assessment

Where would an attacker go next?

  • Stale passwords
  • Over-privileged accounts
  • Compromised passwords
  • Accounts usable for lateral movement
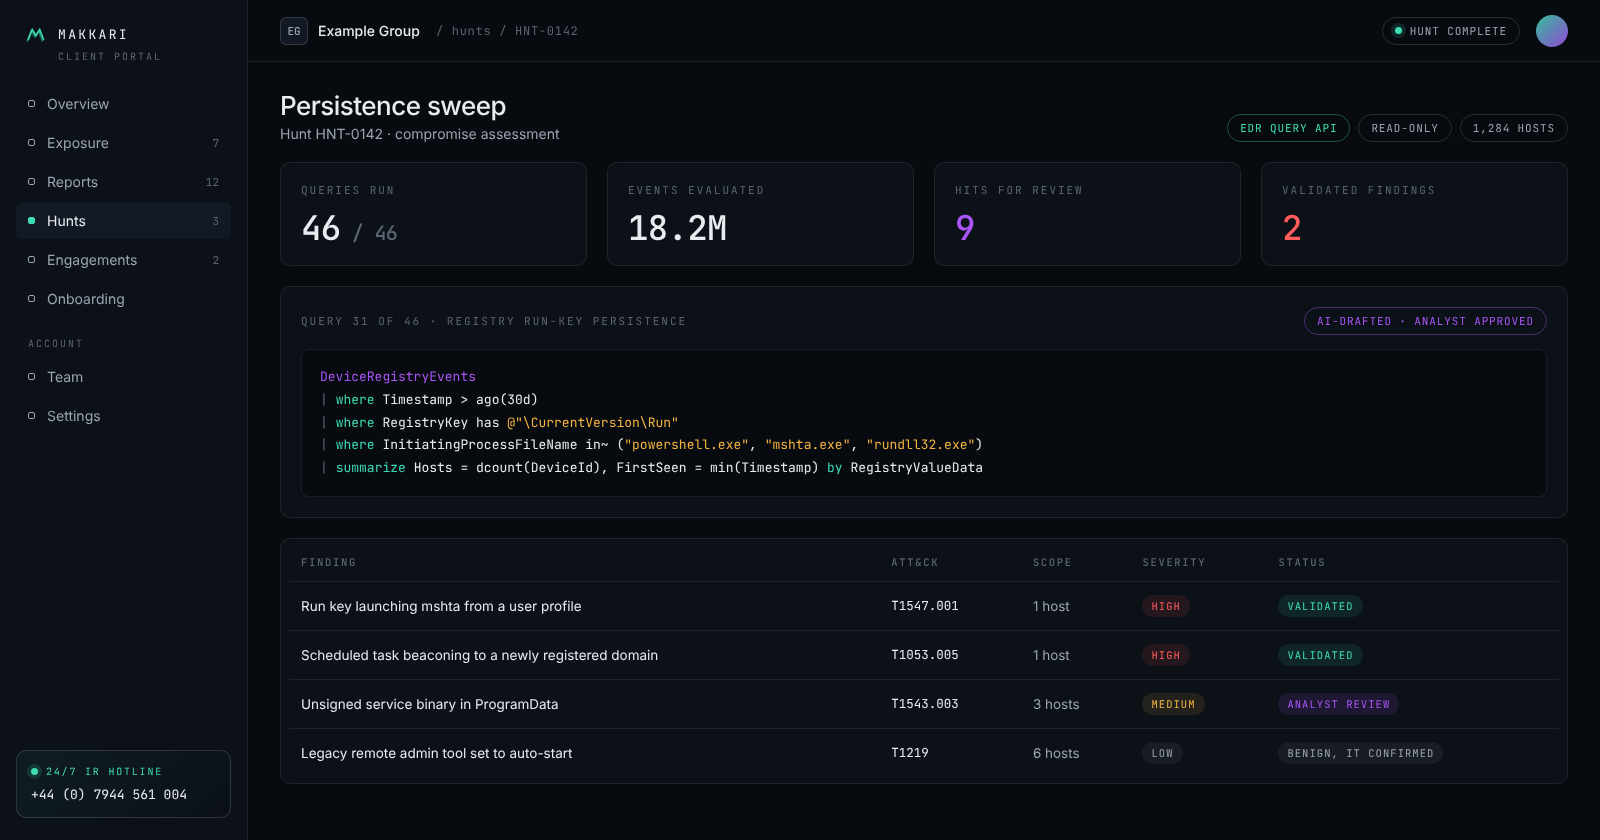
Makkari hunt console showing an EDR query run across the estate and findings awaiting analyst validation
Hunt console · queries run through the client's EDR API, findings validated by an analyst
How it works

Read-only. Nothing installed.

If you run a next-generation EDR with a query API, we hunt through it. AI writes and runs the queries at scale. A senior practitioner confirms every finding before it reaches you.

  • 01Scoped, read-only access
    A time-limited API key. Nothing installed.
  • 02Hunt at scale
    AI drafts and runs queries across every host the EDR can see.
  • 03Human validation
    Every hit reviewed by a practitioner. Noise stays out of the report.
  • 04Report and close
    Findings and fixes delivered in the client portal. Access revoked.
No EDR with a query API?

We deploy a short-term collector for the engagement and remove it at the end.

On a retainer?

Unused Continuum and Vanguard hours can be spent on hunts. See retainers →

Scope a hunt

Tell us about your estate. We will scope the hunt.

Short scoping call, written proposal, no agents to deploy.